Cybersecurity Cannot be an Annual Exercise
If a cyber incident disrupted your institution’s operations for one day, could you quantify the financial impact? Cybersecurity Awareness Month...
4 min read
By Sherah Spark, Chief Risk Officer, CheckAlt
If a cyber incident disrupted your institution’s operations for one day, could you quantify the financial impact? Cybersecurity Awareness Month creates a useful moment to focus on the risks organizations face. But cyber risk and the controls that protect an institution require ongoing attention throughout the year, not only during an annual assessment, audit, or regulatory examination.
As I recently shared with Credit Union Times, cybersecurity now reaches well beyond the IT department. A cyber incident can quickly become a fraud, operational, or business continuity issue. That makes cybersecurity a leadership concern and an everyday operating responsibility.
Most financial institutions already have cybersecurity programs, policies, and formal review processes. Those foundations matter, but they capture the environment at a point in time. Technology changes. Employees take on new responsibilities. Institutions introduce new services, connect with new vendors, revise workflows, and expand the ways data moves across systems. Each change can alter risk exposure before the next scheduled review occurs.
The practical question is not simply whether an institution has cybersecurity controls. Leaders need to know whether those controls reflect how the business operates today, whether they are tested frequently enough, and whether the institution is prepared for the financial and operational consequences if they fail.
A cybersecurity assessment is only as current as the environment it evaluated. A new digital service, system connection, vendor relationship, employee role, or automated workflow can introduce different access requirements, data exchanges, and operational dependencies.
These changes should prompt a security conversation while decisions are still being made. For example, a new digital payment capability may depend on additional system connections or third-party services. Before implementation, leaders should understand what information will move between those systems, who will have access, which controls apply, and how the institution would respond if the service became unavailable.
The goal is not to slow the business down. Bringing risk, security, technology, and business teams together early helps institutions move forward with the right controls in place and avoid costly adjustments later.
Financial institutions can’t manage exposure they can’t see. Data mapping helps leaders understand where sensitive information resides and how it moves through internal systems and third-party environments.
Leaders should be able to answer several practical questions:
Vendor inventories, data maps, and regular access reviews help institutions maintain that visibility as relationships and roles change. This is particularly important because financial institutions depend on technology providers, payment processors, and other partners for critical operations. Leaders need to understand not only a vendor’s security controls, but also the operational dependencies created by the relationship and the vendor’s ability to support recovery.
Having controls documented is not the same as knowing they work. Independent assessments and audits can provide useful external validation, but institutions also need regular testing that reflects their current environment.
Vulnerability scanning and penetration testing can help identify weaknesses across internal infrastructure and customer- and member-facing applications. Testing should examine the systems employees use as well as the portals and applications through which customers and members enter information or access services. The objective is to identify exposure before an attacker does.
Frequency matters. Institutions should determine whether their testing cadence reflects the pace of change in their environment and whether monitoring systems and fraud controls provide sufficient visibility between formal assessments. Monitoring and escalation procedures must also support timely action around the clock.
This is what it means to make cybersecurity part of business as usual: controls operate every day, teams know what they are watching for, and emerging concerns can be escalated before they become larger operational problems.
The human element remains one of the most consequential sources of exposure. Attackers often exploit routine business processes and trusted relationships rather than relying only on a technical vulnerability. A request to update supplier payment information, approve a transaction, share data, or provide access may appear legitimate while redirecting funds or information to a fraudster.
Artificial intelligence is making familiar tactics faster to execute, easier to scale, and more convincing. Attackers can produce realistic messages and impersonate trusted individuals through text, voice, or video. Training therefore needs to keep pace with how employees actually work. Employees should know when to pause, verify a request through another channel, and escalate it for additional review, even when it appears to come from someone they recognize.
AI can also support the institution’s defenses by helping security teams analyze threats, identify potential weaknesses, and prioritize information for review. It should strengthen established security practices and experienced employees, with appropriate governance, access controls, and human oversight.
Cybersecurity investments compete with other business priorities. Leaders are more likely to make informed decisions when they understand the operational and financial consequences of inaction rather than viewing cybersecurity only as a technical requirement.
Leaders should be able to quantify:
Even reasonable estimates can make the risk of inaction more visible. They also give leadership a clearer basis for deciding where investments and attention are most needed.
Cybersecurity will always require specialized technology and expertise, but responsibility for managing cyber risk cannot remain only with IT or information security teams. Business leaders need to understand how their functions depend on technology, data, employees, and third parties and what would happen if those dependencies were disrupted.
A year-round approach doesn’t necessarily require more meetings or more policies. It requires institutions to revisit risk when the business changes, review access regularly, test controls at an appropriate frequency, prepare employees to question trusted requests, and quantify the operational and financial consequences of disruption.
Cybersecurity Awareness Month will end, but the work will not. When cyber risk becomes part of everyday business decisions, financial institutions are better positioned to maintain critical services, prioritize resources, and protect the trust their customers and members place in them.
If a cyber incident disrupted your institution’s operations for one day, could you quantify the financial impact? Cybersecurity Awareness Month...
Progress should be visible in the way clients work. Can they bring new relationships on board faster? Can they put funds to work sooner? Can they...
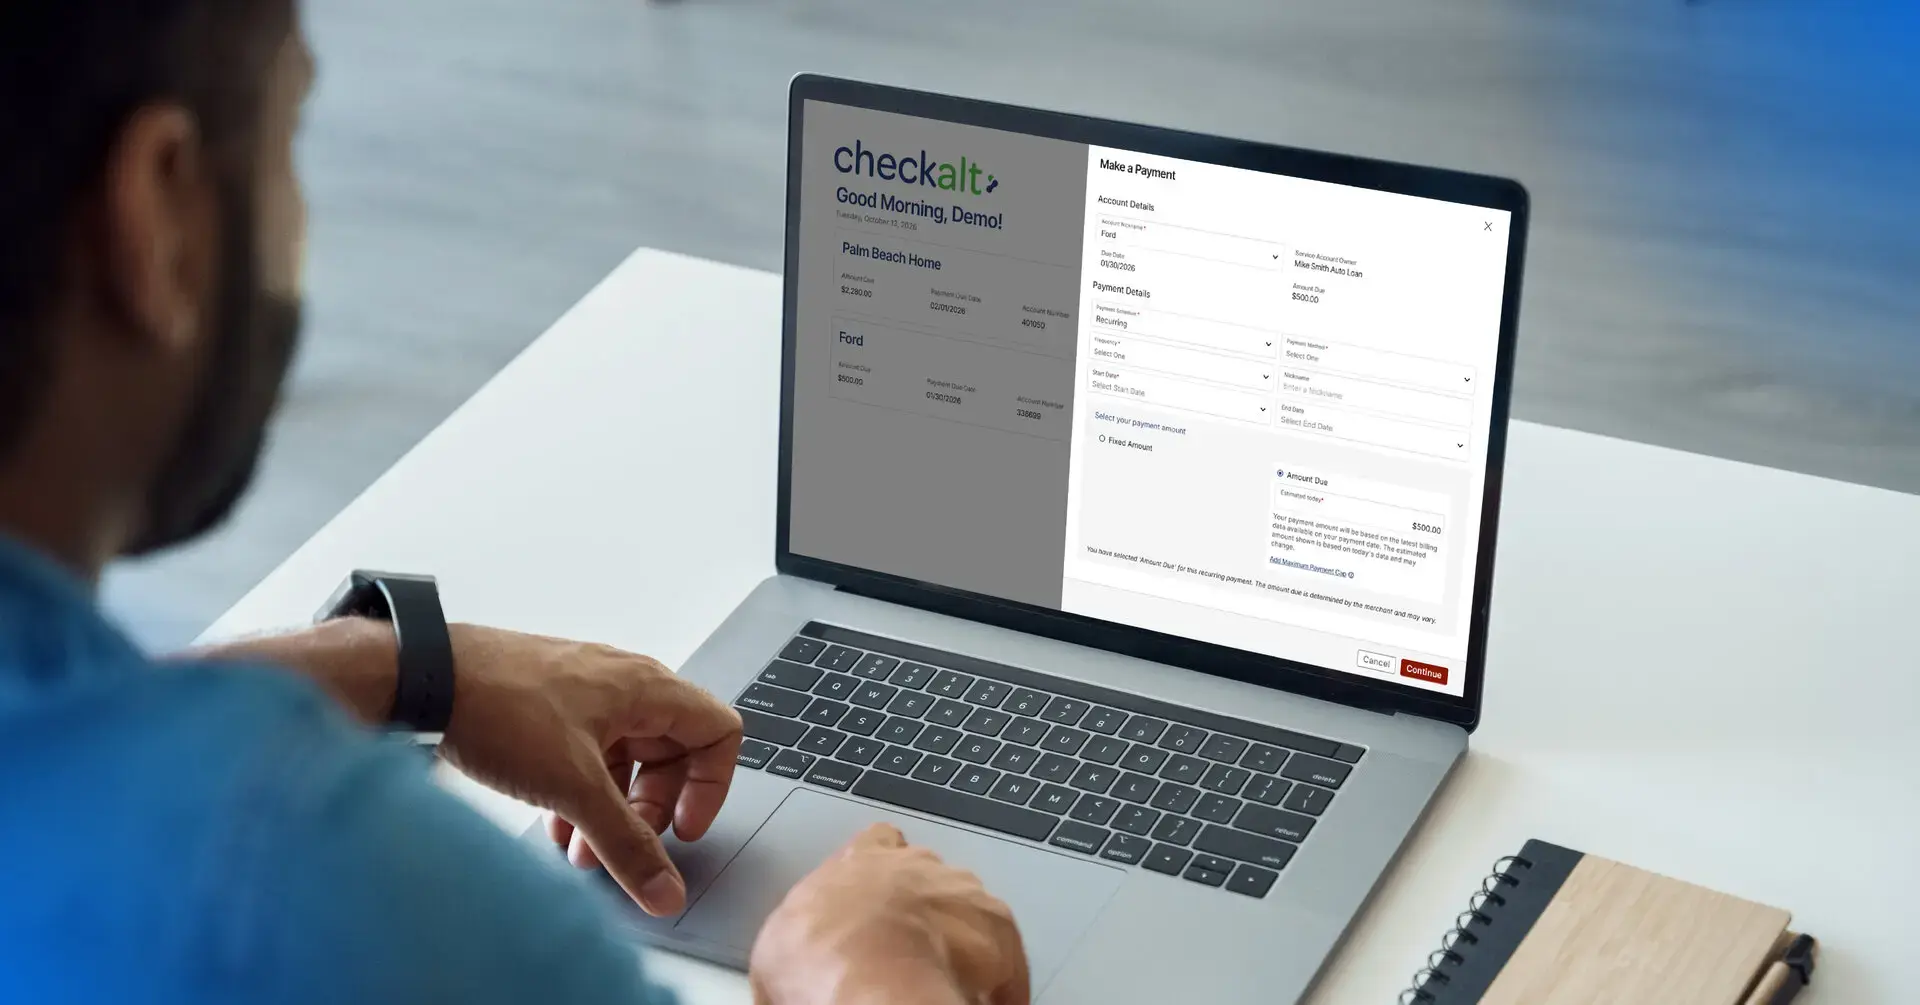
Online payments are a standard part of how consumers and businesses pay bills, invoices, loans, and other obligations. Whether paying a utility bill,...